MalwareCleaning

  • Subscribe to our RSS feed.
  • Twitter
  • StumbleUpon
  • Reddit
  • Facebook
  • Digg
Showing posts with label scam. Show all posts

Tuesday, August 13, 2013

Scams, scams everywhere

Posted on 11:53 PM by Unknown

It's the scam season. Well, actually scams are always going around. Facebook is pretty popular to spread those scams, for example the Gina Lisa Facebook scam and the scam to have Facebook in a different color.

There's one recently that caught my attention:

"This is incredible"


Basically what happened here is that someone on Facebook clicked on the wrong link, and the event got automatically created. Consequently, all of his/her friends were invited to the event as well.

Of the 4 pages that showed up in the search results (there are many more), ~500 people clicked on the bit.ly links. Which is not very much, considering how many people got the invite. Most of the comments on the events were "What is this?", so this means most people realised it's fake.

The CNN logo is being (mis)used, probably to make it look more legit. When you click on the link, you get redirected through affiliates but eventually you land on the following page:


"Dr. Oz Miracle Diet"


Websites:
hxxp://consumerhealthnews9.org  - URLvoid Report
hxxp://consumerhealthnews6.com   - URLvoid Report

When clicking on any of the links on those sites, you get redirect to:
hxxp://ww90.thorizo.net  - URLvoid Report

More affiliates, more links to click on. The title for this blog post could also have been "affiliates, affiliates everywhere". 


Removal

If it seems that you have created the event, simply go to the event page, click the "wheel" icon and choose "Cancel Event":

Cancel the event


Be sure to also check your Apps, it's possible you allowed a malicious app to post & create things on your behalf:

Check your Apps


If you were invited to the event, simply ignore the message. You can also report the event as scam or spam by clicking on the Report button on the left of the event:

Report the event


Conclusion


To keep it short and simple:
don't fall for these types of spam/scam, most of the times it's pretty obvious it's fake.

If in doubt, send your friend on Facebook (or if someone sent you the link) via PM if he or she knows what this is about.

You can also use a linkscanner to verify the integrity of a link on either http://www.urlvoid.com or https://www.virustotal.com/

To get some information on a bit.ly (or other URL shortener services) link, you can use any of the following websites:
- http://www.getlinkinfo.com/
- http://longurl.org/
- http://www.longurlplease.com/ (includes Firefox extension)

To report a malicious bit.ly link use:
http://bitly.com/a/report_spam
Read More
Posted in affiliate, blog update, facebook event, facebook scam, scam, spam | No comments

Monday, June 24, 2013

Gina Lisa Facebook scam

Posted on 2:17 PM by Unknown


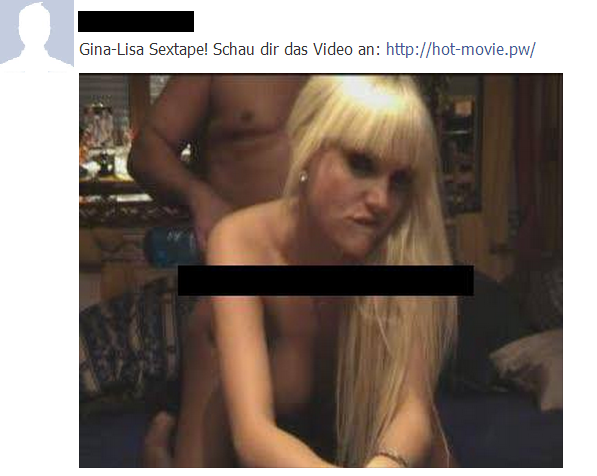
Yet another Facebook scam, this time luring users with a sextape from Gina Lisa, whom is apparently a German model:


Yet another Facebook scam: "Gina Lisa Sextape"


Note I only covered up the profile name & profile picture of the user who posted this, the screenshot from the "video" itself is actually not edited. Not sure what it should be covering up there...

When you click on the link you get:
Verify your age first


When you click on the video to "verify your age" you are redirected to what appears to be a site for gambling, pokergames, etc....:

Subscribe and get a free bonus. Looks legit


I suspect you'll probably have to pay up sooner or later to continue playing. Stargames.com is apparently known for spamming blogs & other sites.

hXXp://hot-movie.pw - URLvoid Report
hXXp://stargames.com - URLvoid Report


Interestingly enough, when I decided to also try and visit the page without a proxy, I got the following warning:

Illegal games much?


This scam and/or spam will also post on Facebook on your behalf. Go over your Privacy Settings on Facebook and make sure you delete this "app" if you see it. Remove any posts you have made as well and report posts similar as this made by your friend(s).


Prevention

Pretty straightforward: do not click on any of these links, how tempting they might be ! Ask your friend if he or she knows what it means, and slightly hover over the post until the 'X' becomes visible. You can then mark the post as spam, and it will be removed from your friend's wall.

It might also help to install the WOT extension into your browser. (Compatible with most modern browsers)
WOT is a community-based tool and is therefore very useful for these kinds of scams, whereas other users can warn you about the validity.
More information and to download WOT: http://www.mywot.com/


Conclusion
To keep it short and simple:
don't fall for these types of spam/scam, most of the times it's pretty obvious it's fake.
Read More
Posted in blog update, facebook, facebook scam, Facebook spam, gina lisa, illegal games, poker games, scam, spam | No comments

Wednesday, February 20, 2013

Facebook in a different color? Nah, just a survey scam

Posted on 7:59 AM by Unknown

I got messaged about an obvious scam on Facebook:


New Facebook colors!


Strangely enough, that person's Facebook color was still in blue. Is it possible this is just a scam? ;-)


Going to the application:

The application "Pick a col0r" requests your permissions


 Next screen....:
I choose the blue color. Oh, right...


You've won!


As with most applications like these, you first have to fill in a survey to get your Facebook in a different color. Obviously, you still won't be able to even if you have filled in all your information for a chance to win product X or Y.


The application will make the same post on your wall as in the first picture. To remove it:

Go to your privacy settings, applications and remove "Pick a C0lor".


Confirm the removal and check the box. 


 Conclusion

You cannot change the color of Facebook at this point, there is no dislike button, ....

All of these 'applications' point to survey scams where you fill in all your information and your inbox will be flooded with spammail. And no, you haven't won anything.


Read More
Posted in blog update, change facebook color, facebook, facebook dislike button, facebook scam, Facebook spam, scam, survey scam | No comments

Thursday, January 17, 2013

About YouTube top comments

Posted on 8:19 AM by Unknown

Have you seen  the top comments on YouTube recently? Mostly, they're about the videoclip itself, or about other artists that do not live up to the talent of said videoclip ;-) .

Sometimes, however, spam reaches the top comments (whether or not with a lot of upvotes):
Another user is being addressed, "confirming" the site is real


I've seen this kind of Youtube spam unfold into 2 scenarios:
1) The usual survey scams, promising an iPad for example
2) The download of adware or a PUP (Potentially Unwanted Program) to your machine


Let's take a look at both scenarios, we will go more in depth about the second one, as it is the most interesting. This post includes prevention methods, a removal process and a conclusion at the bottom if you want to skip the investigation.


Investigation


1) Survey scam

As seen in above picture, another user is being addressed. This user did not make any comments on the video at all. I'm guessing they use this little trick to 'confirm' someone asked about it and they are 'just helping out'. The comment has several upvotes as well, thanks to the use of bots.

Clicking on the bit.ly link, you are being redirected to another website:
hxxp://alllightsfull.info/prize/prize.html
2/30 - URLvoid Result
2/33 - VirusTotal Result
AllLightsFull.info - Whois Record

Screenshot:
Congratulations! You won a... Survey scam!


After clicking on Start Now!, you'll get redirected to fill in a survey for a chance in winning an iPad... Which will redirect you to another survey... To another survey.... Until you need to fill in personal details such as your email address. In my case, I had to subscribe to about 20 other instances (read: Brace yourselves, spam is coming) to win the iPad.

 Obviously, you won't win anything and your email address will end up on several spamlists.


 2) Adware / Potentially Unwanted Program

In this scenario, you end up on a different website, but with a similar, easy layout:
Download Youtube videos with "YouTubeSaved"


Some information about the website:  
hxxp://www.youtubesaved.com 
1/30 - URLVoid Result
0/34 - VirusTotal Result 
YoutubeSaved.com - Whois Record

You can download from Download.com/CNET or directly via their website. I'm not sure what's worse: the fact that you can download this beautiful piece of crap via CNET or that it's Norton/VeriSign Secured.

The following file is downloaded:
cid_185425_sono.exe
Result: 3/46
MD5: a3675a8439b09049a76da7f9c93c4a34
VirusTotal Report
Anubis Report
ThreatExpert Report


In the following minutes, I got several new screens to install additional software:
FLV Media Player coming along with WhiteSmoke


FLV Media Player coming along with PriceGong, Freetwittube,...


Some readers might remember WhiteSmoke from a few years ago, when it came bundled with a rootkit and was particularly annoying as well as hard to remove.

While I was eagerly clicking Next on all of the screens, there were a few connections. In fact, in those 5 minuts of installing FLV Media Player, (and thus also: Yontoo, Relevant Knowledge, Free Ride Games, Moyea, Remote Programs, PriceGong, Conduit and WhiteSmoke) there were about 1140 outbound HTTP requests installing even more adware.

If you're interested in these connections, I have uploaded a Fiddler log to Pastebin:
http://pastebin.com/QxcHca1Z


Interesting to note is that Firefox gave a warning about a particular toolbar:
https://addons.mozilla.org/en/firefox/blocked/i226
From that page:
This add-on is silently side-installed by other software, and doesn't do much more than changing the users' settings, without reverting them on removal.

Actually it does more than that, it redirects your searches (through ad-sponsored networks), changes your homepage, annoys you with pop-ups, .... This does not solely apply to WhiteSmoke.

A total of 63 newly created PE files was found on my machine. Seems like they really wanted me to install as much toolbars and adware as possible. Sometimes, besides being referred to as a PUP or adware, this kind of software is called foistware.

You can find a Pastebin here with all VirusTotal results:http://pastebin.com/87HspUgu


Prevention

Now, how do we prevent these applications from ever entering our system? Here are a few tips:

  • Carefully consider what you are installing. Is this program known at all? What does it do? Do I really need this installed? A simple Google search reveals a lot of answers.
  • Don't click Next, Next, Next or OK to everything or in any of the screens you get. This is a golden rule in general.
  • Read the EULA. No wait, what? Those EULAs are always way too long! That's right, luckily there's a tool available which can assist us in identifying unwanted behaviour. The tools is called EULAlyzer, by the same developer as SpywareBlaster (which also helps prevent these).

    I did a scan on a EULA from PriceGong which uncovered the following results:
    EULA states advertising, your searches being submitted and more


  • Use the extension WOT (Web of Trust) to get a second opinion about website X or Y.
  • If you encounter a link that is shortened (for example bit.ly, t.co, tinyurl, ....) you can use a website as GetLinkInfo or Unshorten to acquire more information on that link. Awesome!


Removal

Of course, it might be too late for some users. They are already seeing pop-ups everywhere, getting amazing deals or are getting redirect in their search engines. Again, you can find some hints:

  • Most of these programs can be easily removed via the Control Panel > Add/Remove Programs. There's also a small guide by Microsoft on how to do that. After uninstallation, these programs will open your browser and offer to reinstall the "product". Just close the browser when that happens.
  • "I removed these programs but am still getting redirected. Why?"
    Probably the Add-On, Extension or Plugin is still installed and active in your browser. Remove or disable this manually by following these steps:
    Removing extensions from Internet Explorer
    Removing extensions from Mozilla Firefox
    Removing extensions from Google Chrome

    Restart your browser afterwards and confirm the changes. It's possible you need to manually reset your homepage as well.

  • "Not everything is gone and I don't see anything in the Add/Remove Programs."
    When this happens, you can use a tool like AdwCleaner. Please keep the following in mind:
    - Close all browsers before executing AdwCleaner
    - Click on Search. A logfile will open. Review this carefully! AdwCleaner is pretty strict in removing adware. Then, you can select delete to delete all the unwanted/malicious entries.
    - More information can be found on the download page of AdwCleaner (see above).
  • After following these steps, use your already installed Antivirus and perform a full scan. When that's finished, you can also use Malwarebytes to perform a Quick Scan and ensure everything is gone. Be sure to select in the Settings tab > Scanner Settings that PUPs are shown in the scan results.
  • If you are having difficulties or are not too sure of following these steps all by yourself, you can always make a post on one of the several forums out there specialized in removing malware and other nonsense from a machine. An example forum where you can get help is BleepingComputer.


Conclusion

After reading this post, I'm sure you can now differentiate the thin line between goodware and foistware, adware, or Potentially Unwanted Programs. With the tips above, you should be able to weapon yourself against this kind of threats.

Some legit programs like Java or Adobe also offer these "toolbars". Don't be fooled! The same above rules should be applied here. Tick off those boxes and read carefully through the installation wizard! Why are these things still around you might ask? There's an interesting article here by Ed Bott:
Why does crapware still exist? Follow the Silicon Valley money trail

You might wonder why your antivirus didn't ring any bells when installing this software. The easy answer is: it is hard to differentiate if this is malicious behaviour, as the users consents and agrees on the EULA - which is basically an agreement to all these unwanted modifications!
The hard and longer answer is something to discuss in a future blogpost.

Conclusion: don't install something when you have no idea what it is or does. Google can be your friend.


Read More
Posted in adware, conduit, flv media player, foistware, potentially unwanted program, pricegong, PUP, scam, spam, whitesmoke, yontoo, youtube, youtube comment spam, youtube spam, youtube top comments | No comments

Wednesday, November 14, 2012

Diablo account phishing

Posted on 6:04 AM by Unknown

Do you love the smell of phishing in the morning? I surely don't. In today's post we will be reviewing a phishing attempt for Diablo or Diablo III.

The following mail ended up in my mailbox:

You need to login as soon as possible to avoid account closing

There are other, less fancy examples:

Same trick as in the previous example. You need to "verify" your account


Subjects of the mail can vary, but these are the most common:
- Blizzard Notification About Diablo III Account
- Diablo III Account-Notice
- Diablo III Account - login validation‏
- You must verify your identity as the registered account .World of  Warcraft - Diablo III account (s).

The introduction in the email reads:

Greetings!   It has come to our attention that you are trying to sell your personal Diablo III account(s). As you may not be aware of, this conflicts with the EULA and Terms of Agreement. If this proves to be true, your account can and will be disabled.  It will be ongoing for further investigation by Blizzard Entertainment's employees. If you wish to not get your account suspended you should immediately verify your account ownership.


Let's move on to the actual link in the phishing mail. When clicked you'll land on the following page:

An exact copy of the real login page at Battle.net


Below you can find the list of URLs I've gathered in the past days, do not visit any of them as they may harm your computer (or even worse, your Diablo account ;-) ).

hxxp://battle.net.noreply-login.com
hxxp://cn15mcc.com
hxxp://eu.diablo.net.account.oy-login.in
hxxp://eu.diablo.net.account.ts-login.in
hxxp://eu.diablo.net.ca.zx-login.in
hxxp://eu.diablo.net.jiagedi.info
hxxp://eu.diablo.net.tianzhou58.info
hxxp://us.battle.com.wwowus.com
hxxp://us.battle.net.w.llweb.asia
hxxp://us.battle.net.ccus.asia
hxxp://us.battle.net.ddeu.asia
hxxp://us.battle.net.eacc.cn.com
hxxp://us.battle.net.en.oo-rs.com
hxxp://us.battle.net.en.qq-rs.com
hxxp://us.battle.net.en.uu-rs.com
hxxp://us.battle.net.ffus.asia
hxxp://us.battle.net.ggwow.asia
hxxp://us.battle.net.hhwow.asia
hxxp://us.battle.net.iieu.asia
hxxp://us.battle.net.llus.asia
hxxp://us.battle.net.login.en.ddus.asia
hxxp://us.battle.net.login.en.yykiki.com
hxxp://us.battle.net.login.en.zkiki.com
hxxp://us.battle.net.ok.jjweb.asia
hxxp://us.battle.net.ok.kk-rs.com
hxxp://us.battle.net.ok.qw-rs.com
hxxp://us.battle.net.ok.uuweb.asia
hxxp://us.battle.net.ok.yywow.asia
hxxp://us.battle.net.ppwow.asia
hxxp://us.battle.net.rreu.asia
hxxp://us.battle.net.uuwow.asia
hxxp://us.battle.net.w.llweb.asia
hxxp://us.battle.net.w-u.asia
hxxp://us.battle.net-bizzard-d3-com.account-com.net
hxxp://us.diablo.net.en.rk-login.in


Most of the domains seem to be set up by the same person, someone named "Jin Yu":
Registrant Contact:
   Jin Yu
   Yu Jin jinyu2000@yahoo.cn
   +86.324242434233 fax: +86.324242434233
   ShengLiLu
   Shangraoshi Jiangxi 610041
   CN

Other email addresses associated with Jin Yu:
329409115@qq.com
service@511web.com


Almost all of the IP addresses are originating from China. The hosting companies are as follows, and seem to not care (or know) that malware and phishing pages are set up:

Beijing Weishichuangjie Technical Development Co. - IPvoid Result
DEEPAK MEHTA FIE - IPvoid Result
New World Telecom Ltd., Hong Kong - IPvoid Result
XIN XIN LING - IPvoid Result


Thanks to IPvoid you can easily see other sites hosted there, seems there is more of the same. (read: more malware & phishing pages are hosted)


Conclusion

Stay away from phishing mails like the ones pointed out in this post. There are several variants, some more graphical than others, but in the end they serve the same purpose:
Trying to steal your login credentials!

I'm sure that even when you open the mail, alarm bells should be going off if you simply check the URL, it's pointing to another address than the usual login page.

To be clear, the real webpage to login for your Battle.net account is:
https://battle.net/login/en/

If you're ever in doubt, visit the website directly and do not click on any links in emails from unknown senders. Use add-ons like WoT and/or NoScript to stay protected against these types of threats.
You can also use the URL scanning services at VirusTotal or URLvoid to double-check a URL.


Read More
Posted in battle.net, blog update, d3, diablo, diablo III, diablo phishing, phishing, scam, spam | No comments

Wednesday, April 11, 2012

Hacked Hotmail accounts... and the consequences

Posted on 4:14 AM by Unknown
It's a trend I'm seeing more and more, even with some of my relatives:

Their Hotmail account is getting hacked, and from then on is being used by scammers or malware authors to spread their malicious intent.

In almost all cases, you'll receive an email with (No Subject), and the only content is a link pointing to some website. But wait: it seems that all those websites have (probably an outdated version of) Wordpress installed.

When you click the link, you will be redirected to either a scam/phishing page or scareware/rogueware.

Either way, you'll first get the following message:


Message you receive when clicking on the link

So let's take a closer look at the 2 scenarios you get on your plate:

Scenario #1 - scam


Scam page

In scenario number one, you'll be presented with an awesome News page, where you can read several testimonials of how great working from home is.

It also has some fascinating news stories on how to make lots of money by simply being at your comfortable home. This includes reactions on the articles - of course this is all fake.

If you click on any of the links on this website, you'll be ultimately redirected to - hxxp://internetprofitpacket.com

Administrative Contact:
WhoisGuard
WhoisGuard Protected
+1.6613102107
Fax: +1.6613102107
11400 W. Olympic Blvd. Suite 200
Los Angeles, CA 90064
US


UrlQuery Result:
Suspicious
http://urlquery.net/report.php?id=40849

URLvoid Result:
1/25 (4.00%)
http://www.urlvoid.com/scan/internetprofitpacket.com/


Ultimately you land on the following page:


Landing page where you'll need to pay

After paying a small price, you'll get lifetime access to the Internet Profit Package ! What honor !

Obviously, you'll get scammed and your credit card details might get stolen.


Scenario #2 - scareware

Likewise as in scenario #1, you'll get the nice message that you got here thanks to your friend.


Seems like you're infected ... right ?

You'll then be presented with a pop-up indicating critical process activity has been found and a scan will be launched... (I think we all know this one by now) :


Fake Explorer window indicating numerous infections

If you click on any button, a file will be downloaded with the name of setup.exe.

In this case, the file was downloaded from:
hxxp://fail-safetylow.info/bb61f9bcec711d56/29/setup.exe

This site and several other rogueware pages are hosted on the IP:
64.120.207.107


Several other rogueware sites are hosted on this IP


We'll now see some more details about the downloaded file:

setup.exe
Result: 5/40
MD5: 8b0c16a50c0bca1eb0b45bd411eb30e5
VirusTotal Report
ThreatExpert Report
Anubis Report

This file drops another executable:

Protector-hfpt.exe
Result: 5/42
MD5: f04cb906356f19a1dbf68c62f162c4e7
VirusTotal Report
Anubis Report


The payload is a rogueware called "Windows Antibreaking System" :


Windows Antibreaking System setup screen


Windows Antibreaking System main screen


Prevention

- Most important of all: use a strong password ! You can verify your current password, or create a new one to check its strength on the following website: http://www.passwordmeter.com

- Second important rule:
don't use the same password for each and every website !

- Be wary when receiving such a mail, even if it's from someone you know.

- Use browser extentions to verify the integrity of an image or URL. Useful add-ons are for example WOT or NoScript.

- Keep your Antivirus and browser, as well as your browser add-ons up-to-date.

- If it is too late and a 'scan' is already starting, immediately close your browser by bringing up Task Manager (CTRL + ALT + DEL) and killing your browser's process:
  • a) For Google Chrome: chrome.exe or chrome.exe *32
  • b) For Mozilla Firefox: firefox.exe or firefox.exe *32
  • c) For Microsoft's Internet Explorer: iexplore or iexplore.exe *32


Desinfection

If the harm is already done and you are getting warnings, messages or pop-ups stating you are infected and you need to take 'immediate action' to clean your computer, follow the guide below at BleepingComputer's to rid yourself of this malware:

BleepingComputer's Virus Removal


Also, if you know the sender personally, notify him/her that they've been hacked and they need to change their password. If you don't know the sender, immediately remove the email.

In Hotmail, you even have a useful option if you know the sender. Open the email, select Mark as and click on My friend's been hacked!


Help your friend by stating (s)he's been hacked


If you happen to have a Wordpress website, be sure to update it regularly as well as any Wordpress plugins you may have installed. This website will aid you in the matter: Hardening WordPress


Conclusion

Don't fall for either of these, in both cases you'll lose a lot of money !

Follow the above prevention tips to decrease the chance of your computer becoming infected.
Read More
Posted in blog update, cracked hotmail, fakeAV, hacked hotmail, Hacked Hotmail accounts, malware, phishing, rogueware, scam, Windows Antibreaking System | No comments

Tuesday, December 6, 2011

New Facebook scam

Posted on 6:26 AM by Unknown
A new Facebook scam is spreading today, 6th of December. The interesting thing is that I have seen it posted in Dutch as well.

The method used is the same as in previous Facebook scams, see for example my earlier post:
New Facebook scam

Here is the post in question (in Dutch):


Classical scam post to lure users into clicking the link.

Here's what it reads:
WOW! Mijn profiel is ALLEEN VANDAAG AL 12 keer bekeken.. en ik kan zien dat er behoorlijk wat stalkers bijzitten LOL! Kijk zelf wie jou allemaal in de gaten houdt op #removed#

In English:

WOW! My profile has been seen 12 time ALREADY ONLY TODAY .. and I can see that quite a few stalkers are included LOL! See for yourself who's keeping an eye on yoy on #removed#


The link has been shortened by the bit.ly URL shortening service. While this service is not malicious on itself, it can also be used by persons with malicious intent, whether it would be hackers, malware authors, ... Or in this case scammers.

Let's review some stats for the bit.ly link first:


98 clicks on this link in the last hour


Top countries, including: France, Germany, The Netherlands


Facebook.com is the most referring site


At the moment of writing, there have been over 1,000 clicks on the link so far. I have already reported it to bit.ly and it should be taken down soon.

UPDATE: bit.ly has already issued a warning for when you click on the link. (12/07/2011)


Now let us analyse where the bit.ly link is taking us. The link can redirect you to different websites, but they will all (so far) redirect you to a page similar to this one (depending on your location):


Who is viewing your Facebook profile ?


You probably don't remember my post from February this year, but the concept is the same: you can supposedly view who's been "stalking", or viewing, your profile. This to attract users on clicking the link. Who doesn't want to see this, right ? Here is my post from early this year:
Facebook rogue applications still lurking around

You can presented with a screen like this (I have several, but I will only post one as example):

Are you the "lucky" winner ?

As stated previously, the concept is the same. Before you can see who's been viewing your profile, you need to fill in a short service to continue.

You may have won a prize, you may have won an iPad, you may have won free ringtones, you may have won a free iPhone application, etc, etc, etc, .... This is of course all a lie.
Remember: if it looks too good to be true, it probably is !

You have to fill in your email address and/or phone number to continue as well. At the end you will end up losing a lot of money, leaving your email address in the open and maybe worse.

Remember: if you click the link while logged in to Facebook, it will also post it on your own wall.


Conclusion

Conclusion is pretty straightforward: do not click on any of the links ! If in doubt, send your friend on Facebook (or if someone sent you the link) via PM if he or she knows what this is about.

To remove this from your or your friend's wall, click on the X on the message, and choose to "Report/Mark as spam" or "Remove Post".

You can also use a linkscanner to verify the integrity of a link on either http://www.urlvoid.com or https://www.virustotal.com/

To get some information on a bit.ly (or other URL shortener serivce) link, you can use any of the following websites:
- http://www.getlinkinfo.com/
- http://longurl.org/
- http://www.longurlplease.com/ (includes Firefox extension)

To report a malicious bit.ly link use:
http://bitly.com/a/report_spam

For any other question, do not hesitate to post a comment !
Read More
Posted in blog update, facebook, phishing, scam, spam, spim | No comments

Sunday, June 19, 2011

New Facebook scam

Posted on 1:11 PM by Unknown
There's a new Facebook scam actively spreading.

Titles as "Monstrously Erotic blonde", "This chick is awesomely crazy" and "Shows her boobs on national TV!" may appeal to the imagination.

Here's some examples:
Example #1

Example #2


Example #3

However, if you click on the link, it will not take you to a Blogger page but instead will redirect you right away to a page where you can see the "video":


You need to click "Jaa" twice to confirm you're over 18


It looks like a legit Facebook page and a Youtube video, but in fact it is all fake. If you click on "Jaa" (which appears to be Finnish for "Share"), you'll see the following page:


Ultimately you need to fill in a survey to see the video


Haven't we seen this type of scam before on Facebook ?
It is similar to the "See who stalks you on Facebook" application that was pretty viral some months ago.
I also made a blog post back then:
http://bartblaze.blogspot.com/2011/02/facebook-rogue-applications-still.html

You need to fill in a survey to see the video. Of course you might be attracted by the chance of winning an iPhone, but it is all fake.

The purpose of these scams are for you to send expensive text messages to 'unlock' the video. Don't be fooled, you'll only lose money by sending text messages !
Additionally, it will also make the same post on your wall (subject & link may vary), so your friends are targeted as well.


Prevention

Pretty straightforward: do not click on any of these links, how tempting they might be ! Ask your friend if he or she knows what it means, and slightly hover over the post until the 'X' becomes visible. You can then mark the post as spam, and it will be removed from your friend's wall.

It might also help to install the WOT extension into your browser. (Compatible with most modern browsers)
WOT is a community-based tool and is therefore very useful for these kinds of scams, whereas other users can warn you about the validity.
More information and to download WOT: http://www.mywot.com/


Conclusion

Although it's been a while since I encountered these types of scams, keep in mind that they may pop-up on your wall one day.

If so, follow the prevention tips mentioned above and all should be fine.


Read More
Posted in blog update, facebook, scam, spam | No comments

Tuesday, February 15, 2011

Facebook rogue applications still lurking around

Posted on 11:16 AM by Unknown

Recently I made a post on Malware Disasters about rogue applications on Facebook.

Here's a small excerpt:

For quite some time now there are rogue applications trying to convince you that you are able to check whoever viewed your profile. There are a lot of different names for this rogue application, some but not all include:


  • creep exterminators
  • catch them being creepy
  • creepy profile peekers
  • privacy bros
  • we catch stalkers


Profile Creeps application


You can read the full article here:
http://malwaredisasters.blogspot.com/2011/02/facebook-rogue-applications-still.html


Conclusion

Conclusion is quite simple: never trust an application on Facebook that promises things that look too good to be true. When things look too good to be true, they probably are ;) .

Always be careful when allowing applications access to your data and/or wall.

Read More
Posted in blog update, facebook, malware, phishing, scam | No comments

Saturday, February 5, 2011

Scam tactic still active

Posted on 1:16 PM by Unknown
In a previous post I already warned you about New scam/phishing tactics .

Recently I received a similar email, telling me my Google Earth boarding pass is ready.
Apparently the same guys are back trying their tactic once again.

The subject of the email was
Google Earth Enhancement: Your Boarding Pass is Ready


Email from 'The Earth Team'


Banner urging you to download the 2011 version


The domain where you can 'buy' Google Earth is listed below. Note it might still be active, so be careful with the link(s).

hxxp://earth-online-locations.com
Result: 1/17 (6 %)
Domain Hash: 080a81b600bddf891a7b473e5958ab9f
URLVoid
VirusTotal


Conclusion

Basically the same as in my previous post. Simply delete the email and don't look back.

If you really want to download Google Earth, you can download it directly (and for free) from http://www.google.com/earth/index.html


Read More
Posted in blog update, google earth, phishing, scam, spam | No comments

Tuesday, November 23, 2010

New scam/phishing tactics

Posted on 12:53 PM by Unknown
Recently I've seen some new scam/phishing tactics rising to the surface:


Email inviting you to download the newest PDF reader


Email inviting you to download Google Earth


Basically they just want you to pay for a product you can download for free. This time it's Adobe PDF Reader and Google Earth that are being targeted.

Be alerted when you receive an email with subjects like:

New 2010 Version for Google Earth
Update to PDF Reader 2010 for Windows‏
Get more out of Google Earth‏
New PDF Reader with Activation Code‏
Update your PDF Reader for Windows
‏


Do not click on any of the links, and don't be fooled if the URL doesn't look 'funny'.
They might use URL shortener services such as bit.ly or tinyurl.com to hide the real URL.

If you are really interested in any of the forementioned applications, go to the original site and download it *for free ;)* from their website.


Screenshot of the 'PDF' website


Screenshot of the 'Google Earth' website


Conclusion

The conclusion is pretty simple: delete these emails and never reply on them !
If you are unsure if the email is legit or not, I would delete it anyway.
For instance: Google will not email you with a request to download their Google Earth application and pay for it.

You can always use URLvoid and VirusTotal URL scanners as a reference.

Be safe people, and don't fall for these tricks.
Read More
Posted in adobe, blog update, google earth, PDF, phishing, scam, spam | No comments
Older Posts Home
Subscribe to: Posts (Atom)

Popular Posts

  • League of Legends RP hack
    I recently blogged about a (still current) scam targeting players of the online game League of Legends: Free Riot codes scam . When re-check...
  • test for the blog
    Just testing ... :-)
  • Facebook Support. Personal data has been changed!
    There appears to be a new malicious email being sent out with the subject: " Facebook Support. Personal data has been changed! ID7530...
  • WinMHR: Free Malware Detector
    Today I checked out WinMHR brought to you by: Team Cymru Now, what exactly is WinMHR ? (This is copied from the website) WinMHR is... Free ...
  • Malware Puzzle
    A malware (crossword) puzzle you say? Yes! Why not? I've made a puzzle about malware (and security) related keywords. It comes in .PNG f...
  • Brazilian banking Trojan tricks
    So I encountered what I suspect to be a banker focused on Brazilian banks. (Win32/Bancos) Part 1 - spam mail : Fiscal note Mail from: mail.u...
  • Increase in Dutch banking phishing
    Recently I made a post on Malware Disasters about an increase of targeted phishing in the last few monts. The focus was mainly on Dutch (an...
  • Gina Lisa Facebook scam
    Yet another Facebook scam, this time luring users with a sextape from Gina Lisa, whom is apparently a German model: Yet another Facebook sca...
  • A word on XDocCrypt/Dorifel/Quervar
    I'm sure everyone has heard by now about the so called XDocCrypt/Dorifel/Quervar malware. It has mostly damaged machines in The Netherla...
  • FedEx spam loads malware
    Received an email from (supposedly) FedEx today, seems my parcel was unable to be delivered: Print your receipt!     Mail details: Subject: ...

Categories

  • ACH transfer
  • adobe
  • adobe exploit
  • ADP
  • adware
  • affiliate
  • all your data are belong to us
  • antimalware
  • asprox
  • bancos
  • banking trojan
  • basic malware cleaning
  • battle.net
  • blackhole exploit kit
  • blog update
  • botnet
  • brazilian banking trojan
  • brucon
  • change facebook color
  • conduit
  • cracked hotmail
  • credit card blocked
  • crimeware kit
  • CVE-2006-0003
  • CVE-2010-0840
  • CVE-2012-4681
  • cybercrime
  • d3
  • diablo
  • diablo III
  • diablo phishing
  • DLL injection
  • Dorifel
  • dorkbot
  • encryption
  • end of july
  • exploit
  • exploit kit
  • exprez
  • facebook
  • facebook dislike button
  • facebook event
  • facebook scam
  • Facebook spam
  • facepalm
  • Fake Symantec security check
  • fakeAV
  • fareit
  • FedEx
  • FedEx spam
  • first post
  • flv media player
  • foistware
  • free riot code scam
  • free riot codes
  • free riot points
  • free riot points scam
  • free RP generator
  • fun
  • gina lisa
  • google earth
  • google image poisoning
  • google images
  • hacked hotmail
  • Hacked Hotmail accounts
  • hakin9
  • Hewlett-Packard ScanJet
  • hotfile
  • hotmail
  • illegal games
  • infostealer
  • ING
  • IP and RP Hack Download
  • java
  • java exploit
  • kuluoz
  • lame old malware
  • League of Legends
  • League of Legends MultiHack Generator
  • League of Legends RP generator
  • League of Legends RP hack
  • linkedIN
  • LoL
  • LoL RP Hack
  • low detection
  • malvertising
  • malware
  • malware analysis
  • malware analysis lab
  • malware cleaning
  • malware lab
  • malware puzzle
  • malware tools
  • medfos
  • messenger
  • MSN
  • neosploit exploit kit
  • paypal
  • paypal spammail
  • PC Speed Maximizer
  • pcspeedplus
  • PDF
  • phishing
  • poker games
  • potentially unwanted program
  • pricegong
  • PUP
  • pushdo
  • Quervar
  • Question and Answer
  • rabobank
  • ransomware
  • rapidshare
  • redkit exploit kit
  • RemovalTool.exe
  • Riot codes scam
  • Riot points scam
  • roguevertising
  • rogueware
  • rootkit
  • sasfis
  • scam
  • scareware
  • security
  • security conference
  • security.nl
  • skype
  • skype worm
  • social engineering
  • spam
  • spear phishing
  • spim
  • survey scam
  • team cymru
  • technoviking
  • tepfer
  • test
  • trojan
  • twitter
  • United Parcel Service
  • UPS
  • UPS spam
  • verizon spam
  • video
  • vmware
  • wellsfargo
  • whitesmoke
  • Windows Antibreaking System
  • windows live
  • WinMHR
  • worm
  • XDocCrypt
  • yontoo
  • youtube
  • youtube comment spam
  • youtube spam
  • youtube top comments
  • zeus

Blog Archive

  • ▼  2013 (18)
    • ▼  September (2)
      • Malware: the blame game
      • PayPal spam leads to malware cocktail
    • ►  August (2)
    • ►  July (1)
    • ►  June (3)
    • ►  May (2)
    • ►  April (1)
    • ►  March (1)
    • ►  February (3)
    • ►  January (3)
  • ►  2012 (14)
    • ►  November (1)
    • ►  October (2)
    • ►  September (2)
    • ►  August (3)
    • ►  July (1)
    • ►  June (2)
    • ►  April (3)
  • ►  2011 (15)
    • ►  December (1)
    • ►  September (1)
    • ►  June (1)
    • ►  April (3)
    • ►  March (1)
    • ►  February (5)
    • ►  January (3)
  • ►  2010 (14)
    • ►  December (3)
    • ►  November (1)
    • ►  October (6)
    • ►  September (2)
    • ►  August (1)
    • ►  March (1)
Powered by Blogger.

About Me

Unknown
View my complete profile