MalwareCleaning

  • Subscribe to our RSS feed.
  • Twitter
  • StumbleUpon
  • Reddit
  • Facebook
  • Digg
Showing posts with label credit card blocked. Show all posts

Friday, September 2, 2011

Increase in malicious spam

Posted on 7:10 AM by Unknown


Rodel Mendrez from M86 Security labs has made an excellent post on a Massive Rise in Malicious Spam:

http://labs.m86security.com/2011/08/massive-rise-in-malicious-spam/


As he notes in his conclusion, "It seems spammers have returned from a holiday break and are enthusiastically back to work."


So I decided to check out if I had received some spam as well. Jackpot ;-) !


UPS notification


Re: End of July Statement Required


Your credit card has been blocked


ACH Transfer Review


Most of the files are displaying a Word or PDF icon to trick

the user in opening the file:


Some examples of attachments, with their respective

VirusTotal results:


Invoice_08.17.2011_Collcod.exe

MD5: cf0397bb622e4ed9dfdeb07fcbfa9687

VirusTotal Report


MasterCard_invoce_ID73284783275943.doc.exe

MD5: 0b7eba77dd4bcea3c670c4a664e98778

VirusTotal Report


UPS_Document.exe

MD5: 17f9148b130a94ab1f50030ebbf2415a

VirusTotal Report


form-62091.exe

MD5: e18d8cb2a4264a3c559d7967b3c6ab99

VirusTotal Report


When opening either of these files, you can end up with a rogue.

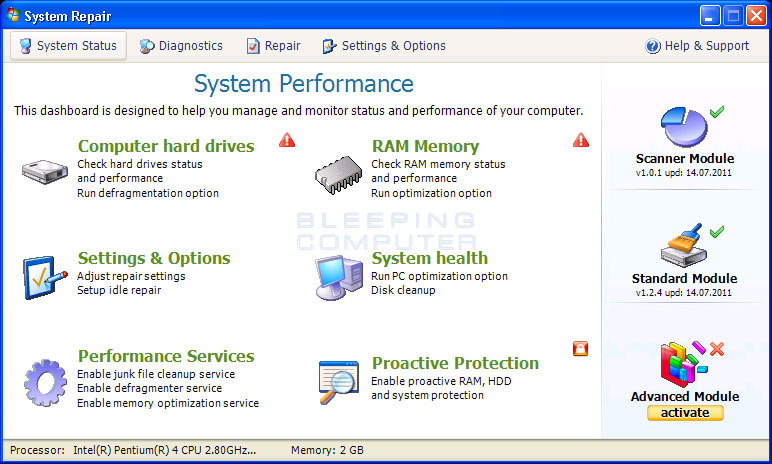
One example rogueware I got was "System Repair":


System Repair rogueware


The dropped file that is launching the rogueware:


pusk3.exe

MD5: 27077c2058983bb76bd09cdad69f7bde

Result: 36/44 (81.8%)

VirusTotal
Report

ThreatExpert
Report

Anubis Report


Conclusion

Conclusion is pretty simple: Do not open any attachments from unknown senders.

If you happen to be infected with System Repair, you can for example use the guide on Bleepingcomputer:

http://www.bleepingcomputer.com/virus-removal/remove-system-repair


Read More
Posted in ACH transfer, blog update, credit card blocked, end of july, FedEx, malware, spam, UPS | No comments
Older Posts Home
Subscribe to: Posts (Atom)

Popular Posts

  • League of Legends RP hack
    I recently blogged about a (still current) scam targeting players of the online game League of Legends: Free Riot codes scam . When re-check...
  • test for the blog
    Just testing ... :-)
  • Facebook Support. Personal data has been changed!
    There appears to be a new malicious email being sent out with the subject: " Facebook Support. Personal data has been changed! ID7530...
  • WinMHR: Free Malware Detector
    Today I checked out WinMHR brought to you by: Team Cymru Now, what exactly is WinMHR ? (This is copied from the website) WinMHR is... Free ...
  • Malware Puzzle
    A malware (crossword) puzzle you say? Yes! Why not? I've made a puzzle about malware (and security) related keywords. It comes in .PNG f...
  • Brazilian banking Trojan tricks
    So I encountered what I suspect to be a banker focused on Brazilian banks. (Win32/Bancos) Part 1 - spam mail : Fiscal note Mail from: mail.u...
  • Increase in Dutch banking phishing
    Recently I made a post on Malware Disasters about an increase of targeted phishing in the last few monts. The focus was mainly on Dutch (an...
  • Gina Lisa Facebook scam
    Yet another Facebook scam, this time luring users with a sextape from Gina Lisa, whom is apparently a German model: Yet another Facebook sca...
  • A word on XDocCrypt/Dorifel/Quervar
    I'm sure everyone has heard by now about the so called XDocCrypt/Dorifel/Quervar malware. It has mostly damaged machines in The Netherla...
  • FedEx spam loads malware
    Received an email from (supposedly) FedEx today, seems my parcel was unable to be delivered: Print your receipt!     Mail details: Subject: ...

Categories

  • ACH transfer
  • adobe
  • adobe exploit
  • ADP
  • adware
  • affiliate
  • all your data are belong to us
  • antimalware
  • asprox
  • bancos
  • banking trojan
  • basic malware cleaning
  • battle.net
  • blackhole exploit kit
  • blog update
  • botnet
  • brazilian banking trojan
  • brucon
  • change facebook color
  • conduit
  • cracked hotmail
  • credit card blocked
  • crimeware kit
  • CVE-2006-0003
  • CVE-2010-0840
  • CVE-2012-4681
  • cybercrime
  • d3
  • diablo
  • diablo III
  • diablo phishing
  • DLL injection
  • Dorifel
  • dorkbot
  • encryption
  • end of july
  • exploit
  • exploit kit
  • exprez
  • facebook
  • facebook dislike button
  • facebook event
  • facebook scam
  • Facebook spam
  • facepalm
  • Fake Symantec security check
  • fakeAV
  • fareit
  • FedEx
  • FedEx spam
  • first post
  • flv media player
  • foistware
  • free riot code scam
  • free riot codes
  • free riot points
  • free riot points scam
  • free RP generator
  • fun
  • gina lisa
  • google earth
  • google image poisoning
  • google images
  • hacked hotmail
  • Hacked Hotmail accounts
  • hakin9
  • Hewlett-Packard ScanJet
  • hotfile
  • hotmail
  • illegal games
  • infostealer
  • ING
  • IP and RP Hack Download
  • java
  • java exploit
  • kuluoz
  • lame old malware
  • League of Legends
  • League of Legends MultiHack Generator
  • League of Legends RP generator
  • League of Legends RP hack
  • linkedIN
  • LoL
  • LoL RP Hack
  • low detection
  • malvertising
  • malware
  • malware analysis
  • malware analysis lab
  • malware cleaning
  • malware lab
  • malware puzzle
  • malware tools
  • medfos
  • messenger
  • MSN
  • neosploit exploit kit
  • paypal
  • paypal spammail
  • PC Speed Maximizer
  • pcspeedplus
  • PDF
  • phishing
  • poker games
  • potentially unwanted program
  • pricegong
  • PUP
  • pushdo
  • Quervar
  • Question and Answer
  • rabobank
  • ransomware
  • rapidshare
  • redkit exploit kit
  • RemovalTool.exe
  • Riot codes scam
  • Riot points scam
  • roguevertising
  • rogueware
  • rootkit
  • sasfis
  • scam
  • scareware
  • security
  • security conference
  • security.nl
  • skype
  • skype worm
  • social engineering
  • spam
  • spear phishing
  • spim
  • survey scam
  • team cymru
  • technoviking
  • tepfer
  • test
  • trojan
  • twitter
  • United Parcel Service
  • UPS
  • UPS spam
  • verizon spam
  • video
  • vmware
  • wellsfargo
  • whitesmoke
  • Windows Antibreaking System
  • windows live
  • WinMHR
  • worm
  • XDocCrypt
  • yontoo
  • youtube
  • youtube comment spam
  • youtube spam
  • youtube top comments
  • zeus

Blog Archive

  • ▼  2013 (18)
    • ▼  September (2)
      • Malware: the blame game
      • PayPal spam leads to malware cocktail
    • ►  August (2)
    • ►  July (1)
    • ►  June (3)
    • ►  May (2)
    • ►  April (1)
    • ►  March (1)
    • ►  February (3)
    • ►  January (3)
  • ►  2012 (14)
    • ►  November (1)
    • ►  October (2)
    • ►  September (2)
    • ►  August (3)
    • ►  July (1)
    • ►  June (2)
    • ►  April (3)
  • ►  2011 (15)
    • ►  December (1)
    • ►  September (1)
    • ►  June (1)
    • ►  April (3)
    • ►  March (1)
    • ►  February (5)
    • ►  January (3)
  • ►  2010 (14)
    • ►  December (3)
    • ►  November (1)
    • ►  October (6)
    • ►  September (2)
    • ►  August (1)
    • ►  March (1)
Powered by Blogger.

About Me

Unknown
View my complete profile